BreakingPage 7
277 articles · newest first · page 7 of 12
Fast-turnaround coverage of active threats as they develop — APTs, ransomware gangs, breaches.
VMware vCenter Exploit Deploys Reverse SSH Backdoor
Threat actors exploiting CVE-2026-59310 are deploying a reverse SSH tool for persistent access on compromised vCenter management planes.

Trezor Breach: 14,000 Customers Exposed via ShipMonk Hack
Trezor disclosed a breach hitting nearly 14,000 customers after shipping partner ShipMonk was compromised. No device or key exposure. Customer order data is the risk.

White House Opens Hack-Back Program to Private Firms
Trump memo directs the NCC to license private security firms for offensive cyber ops against foreign criminal organizations. $1M bond required for compliance.

Jewelbug APT Merges Espionage and Crypto Fraud
Symantec links China-tied Jewelbug to dual operations — state espionage and cryptocurrency fraud — run from the same C2 web panel, with a victim database logging over one million implant check-ins.
Fortinet Patches Critical FortiWeb Auth Bypass, CVSS 9.8
CVE-2026-26035 in FortiWeb lets unauthenticated attackers log in with any credentials — CVSS 9.8. FortiManager also gets a CVSS 8.1 auth bypass fix this cycle.
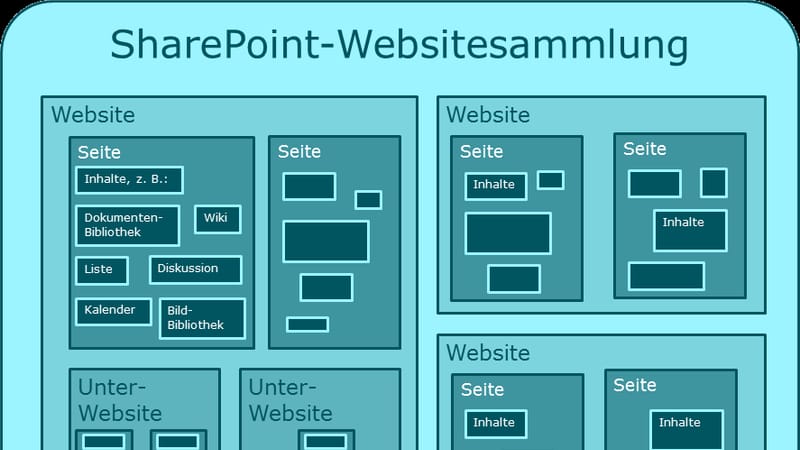
SharePoint CVE-2026-55040 Exploited After PoC Drop
Rapid7's 30-day embargo on CVE-2026-55040 has expired. A public PoC is circulating and active exploitation is confirmed. The July 2026 CU patches it. Apply it now.
Android Malware Relays NFC Cards, Takes Out Loans
WindRelay, a new Android NFC relay malware, is deployed alongside SpyNote RAT to steal live card data and take out fraudulent loans in victims' names.

Colombia Justice Ministry Hit With Ransomware
Ransomware disrupted Colombia's Ministry of Justice days before the presidential transition, part of a documented pattern of attacks on Latin American government institutions.
Attackers Exploiting Critical Adobe Commerce Flaw
Active exploitation of CVE-2026-71362 targets Adobe Commerce and Magento storefronts. CVSS 9.1 critical flaw enables account hijacking without user interaction.
Lazarus Targeted Defense Firms via Windows Zero-Day
Lazarus exploited a Windows zero-day in afd.sys targeting defense firms via Operation Dream Job. CISA issued a two-week federal patch mandate.
ShieldBreak: Defender Patch Bypass PoC Published
ShieldBreak PoC, released hours after Patch Tuesday, claims to bypass the CVE-2026-50656 Defender fix and achieve SYSTEM access on patched systems.
vCenter Auth Bypass CVE-2026-59310 Now Exploited
CVE-2026-59310 exploitation confirmed in VMware vCenter Server. CVSS 9.8. Patches out since July 29 — unpatched instances need isolation now.
SAP Commerce Cloud CVSS 10 RCE — Patch Released
SAP patches CVE-2026-58231, a CVSS 10.0 unauthenticated RCE in Commerce Cloud's Data Hub Adapter. Apply the fix now or take the component offline.

Ransomware Gang Seizes Hospital's Facebook Page
Ransomware attackers hijacked a hospital system's Facebook page during an active breach, claiming 6TB including mental health, abortion, and sexual assault records.

DeadLock Moves Extortion Infra to Polygon Blockchain
DeadLock ransomware has shifted victim comms and data-leak ops to Polygon smart contracts and Session messaging to resist law enforcement seizures.
CISA: Ransomware Gangs Now Exploiting SonicWall SMA1000
CISA confirmed ransomware operators are actively exploiting CVE-2026-15409 (CVSS 10.0) and CVE-2026-15410 in unpatched SonicWall SMA1000 appliances. Patch has been available since July 14.

Metabase Patches CVSS 10 Zero-Day Under Active Exploit
Metabase has released a patch for the max-severity unauthenticated SQL injection zero-day confirmed in active exploitation since August 8. Update now. No CVE assigned yet.

Levi Strauss Breach: Social Engineering, Data Exfil
A threat actor used social engineering to compromise three Levi Strauss employee computers and exfiltrate corporate data. Scope and attribution unconfirmed.

Three CVEs Chain to Admin Takeover in WordPress Login Plugin
Three CVEs in the Login & Register Forms WordPress plugin before 4.0.2 enable unauthenticated account takeover, including site admins. Update now.
Perl Heap OOB in Regex Engine Through 5.45.1
CVE-2026-15534: signed 32-bit overflow in Perl's superlinear regex cache enables heap OOB on attacker-controlled input. Patch exists; CVSS pending.
Apache Tomcat EncryptInterceptor Bypass Added to KEV — Patch by Aug 7
CVE-2026-34486 lets attackers bypass Tomcat's EncryptInterceptor, exposing clustered node traffic. CISA added it to KEV on Aug 4 after active exploitation. Fixed builds are out.
ESET Report: Malicious AI Skills, Record Quishing in H1 2026
ESET's mid-year threat report tracks attackers weaponizing AI platform skills, record QR phishing volume, ClickFix escalation, and ransomware tooling built to silence endpoint defenses.
Device Code Phishing Reaches Industrial Scale
OAuth device authorization flow abuse has scaled from red-team niche to industrial-scale enterprise credential theft in under six months, per threat researchers.
Midnight Blizzard Uses Hotel Wi-Fi to Deploy CornFlake RAT
Microsoft attributes CaptiveCrunch to Storm-2945, a Midnight Blizzard sub-cluster delivering CornFlake RAT via fake browser updates on hijacked hotel Wi-Fi.