News archive Page 19
918 articles · sorted newest first · page 19 of 39
Looking for a specific story? Search and filter the full archive.

Scottish Crown Office Breach May Spread Across Agencies
Scotland's Crown Office confirms a data breach via a compromised third-party service provider. Investigators warn other government agencies may share the exposure.

Seven Arrested in €30M Commerzbank Account Fraud
German BKA and Brazil's federal police arrested seven over a service provider flaw that enabled withdrawals from Commerzbank customer accounts. €30M stolen.

France Confirms DGFIP Breach; Hacker Claims 600K
France's tax authority confirms unauthorized access in late June via credential theft. A threat actor claims 600,000 records stolen. Investigation ongoing.

AmnesiaStealer Hijacks macOS Browser Sessions
Jamf finds AmnesiaStealer: macOS infostealer that hijacks live browser sessions, steals keychain data, and destroys saved passwords via ClickFix terminal prompts.

macOS Screen Sharing Auth Bypass Exploited in Wild
Netherlands NCSC confirms active exploitation of a macOS Screen Sharing authentication bypass after public PoC release. Attackers deploying Monero cryptocurrency miners.
SAP Commerce Cloud RCE Exploit Hits Days After Patch
Defused flagged active exploitation of a max-severity SAP Commerce Cloud RCE within 72 hours of patching. Unpatched instances are live targets now.

Clop Claims 89GB Shell Theft; Investigation Open
Shell confirms investigating a potential incident after Clop listed the oil giant on its extortion site, claiming 89GB of exfiltrated data. No breach confirmed; initial access vector undisclosed.

ShinyHunters Hits RingCentral: 1.6M Accounts Exposed
ShinyHunters breached RingCentral in July, exposing 1.6 million accounts. Names, addresses, emails, and phone numbers are now published by the group.
Beacon CRM Breach Hits 1,000+ Charities via AWS Key
Over 1,000 UK charities had supporter data exposed after attackers used an AWS access key found in Beacon's public JavaScript build artifacts.

WordPress 7.0.4 Patches High-Severity RCE Flaw
WordPress 7.0.4 fixes a high-severity RCE allowing Author-level accounts to execute code via malicious PostScript files. Update now.

GeoServer Zero-Day SQL Injection Exploited in Wild
Threat actors are actively exploiting an unpatched SQL injection in GeoServer that enables remote code execution. No patch available; restrict exposure immediately.

Apple Notifies Users of Mercenary Spyware Attacks
Apple issued Threat Notifications to iPhone users warning of active mercenary spyware attacks. If you received one, here is what to do immediately.

Belgium eID Browser Extension Bugs Enable RCE
Severe vulnerabilities in Belgium's eID browser extension fully compromised the country's national identity trust framework, researchers confirmed, opening citizen accounts to remote code execution.
Microsoft Patches LegacyHive Windows Zero-Day
Microsoft issued a patch for LegacyHive, a named Windows zero-day disclosed in the gap between July and August Patch Tuesday cycles.

Akira Disables EDR via Safe Mode Reboot, Steals Data
An Akira ransomware affiliate rebooted a compromised host into Safe Mode to kill EDR, exfiltrated data, then failed to encrypt. The exfiltration is the real threat.
VMware vCenter Exploit Deploys Reverse SSH Backdoor
Threat actors exploiting CVE-2026-59310 are deploying a reverse SSH tool for persistent access on compromised vCenter management planes.

New Mirai Variant Adds Encrypted C2 and Credential Sniffer
A new Mirai variant adds encrypted C2 comms and a default-credential sniffer — raising the detection bar for defenders relying on network-layer visibility.

Trezor Breach: 14,000 Customers Exposed via ShipMonk Hack
Trezor disclosed a breach hitting nearly 14,000 customers after shipping partner ShipMonk was compromised. No device or key exposure. Customer order data is the risk.

White House Opens Hack-Back Program to Private Firms
Trump memo directs the NCC to license private security firms for offensive cyber ops against foreign criminal organizations. $1M bond required for compliance.

Jewelbug APT Merges Espionage and Crypto Fraud
Symantec links China-tied Jewelbug to dual operations — state espionage and cryptocurrency fraud — run from the same C2 web panel, with a victim database logging over one million implant check-ins.
Fortinet Patches Critical FortiWeb Auth Bypass, CVSS 9.8
CVE-2026-26035 in FortiWeb lets unauthenticated attackers log in with any credentials — CVSS 9.8. FortiManager also gets a CVSS 8.1 auth bypass fix this cycle.
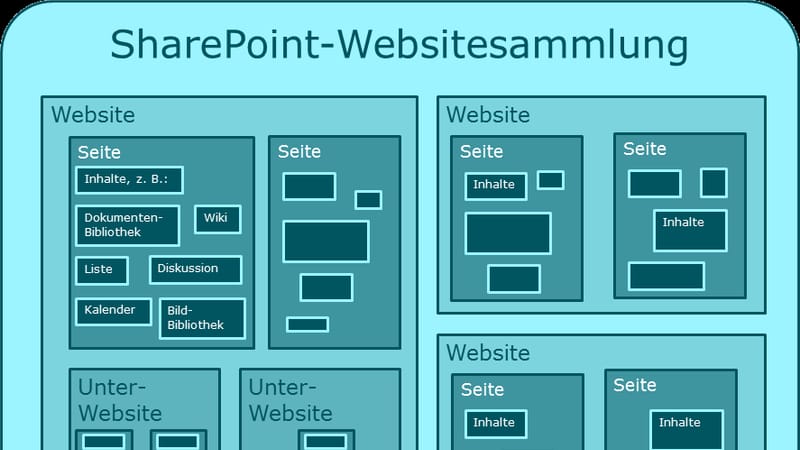
SharePoint CVE-2026-55040 Exploited After PoC Drop
Rapid7's 30-day embargo on CVE-2026-55040 has expired. A public PoC is circulating and active exploitation is confirmed. The July 2026 CU patches it. Apply it now.

ICS Patch Tuesday: Siemens, Schneider, Phoenix Contact
Siemens, Schneider Electric, and Phoenix Contact issued security bulletins on August 12. CISA published parallel ICS advisories the same day. OT operators should review now.
Android Malware Relays NFC Cards, Takes Out Loans
WindRelay, a new Android NFC relay malware, is deployed alongside SpyNote RAT to steal live card data and take out fraudulent loans in victims' names.