MCP Servers
Vulnerabilities in Model Context Protocol (MCP) servers — the integration layer connecting large language models to external data sources and APIs. Recurring classes include server-side request forgery (SSRF), path traversal, and injection flaws across open-source MCP projects deployed as AI infrastructure sidecars.
Latest MCP Servers coverage
Our reporting filed under MCP Servers, plus any story that cites one of its CVEs.
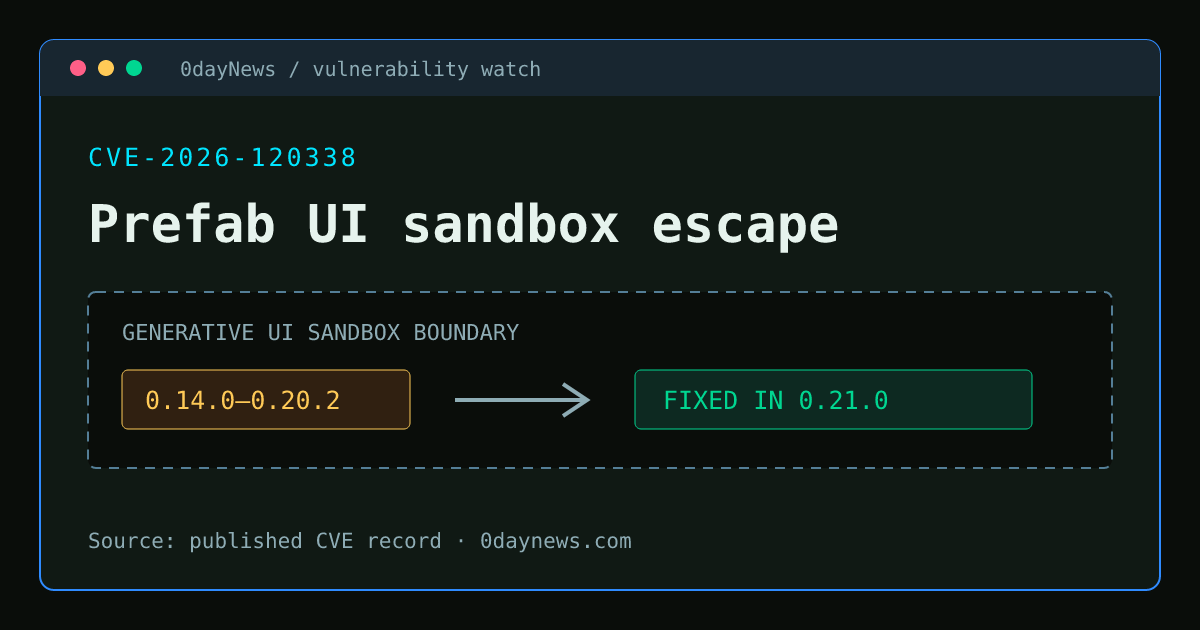
Prefab UI sandbox escape fixed in 0.21.0
CVE-2026-120338 affects Prefab UI's optional Generative UI sandbox in versions 0.14.0 through 0.20.2. The 0.21.0 release contains the fix.
Obot AI Platform Patches Three CVEs, Two Critical
Three GitHub Security Advisories disclose an unauthenticated Docker exposure and two MCP endpoint access control failures in the Obot AI agent platform.
Unauth Access to AI Memory: CVE-2026-50027 Patched
CVE-2026-50027: mcp-memory-service exposed all /api/documents/* routes without auth, letting anyone read, write, or delete AI memories. Patch to 10.67.1.
Ten MCP Server CVEs Drop in a Single Day
Ten MCP server CVEs hit NVD on August 9 — all SSRF or path traversal. Same two classes, ten different projects, most maintainers silent on coordinated disclosure.
Every CVE row links to its record with the CISA required action, catalog coverage and primary sources. We describe impact and remediation only; no exploit code. See the full KEV tracker, the vendor scorecard, or all vendors.