Prefab UI sandbox escape fixed in 0.21.0
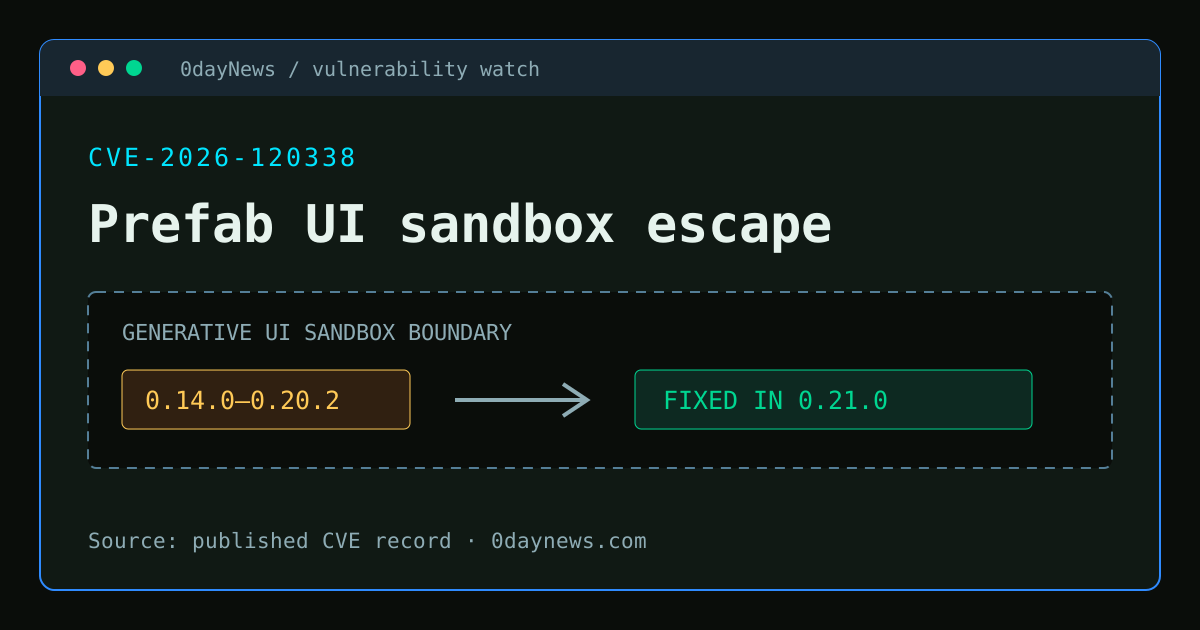
CVE-2026-120338 affects Prefab UI's optional Generative UI sandbox in versions 0.14.0 through 0.20.2. The 0.21.0 release contains the fix.
 Dave "Kilobaud" Ferris
Prefab UI’s optional Generative UI sandbox could let supplied Python code reach files on the server running it. The published CVE-2026-120338 record places the flaw in prefab-ui versions 0.14.0 through 0.20.2 and identifies 0.21.0 as the fix. PrefectHQ released that version on October 26, before the CVE was published on November 1.
The vulnerable feature runs Python in Pyodide, inside a Deno subprocess. The CVE record says the affected sandbox gave that subprocess broad file and network permissions while exposing the Deno API to the Python code. A caller able to submit code could cross the intended boundary and act with the server process’s file permissions. The record also describes a route to persistent host code execution. We are omitting the mechanics of that route; operators need to know which deployments are exposed and which release closes it.
Who needs to check
The CVSS 3.1 score of 10.0 belongs to a specific scenario in the CVE record: a FastMCP server with Generative UI enabled, Deno installed, and no authentication configured. For an authenticated client that is allowed to call tools, the same record gives a separate 9.9 score. Generative UI is opt-in, so the headline score alone does not establish that an arbitrary Prefab UI installation is reachable from the network.
Check whether a deployment uses the Generative UI provider, whether Deno is installed, and who can reach the server or call its tools. Then check the installed prefab-ui version. If it falls in the affected range, upgrade to 0.21.0 or later. The release notes describe sandbox lifecycle changes but do not label them as a security fix; the CVE record links those changes to the vulnerability.
The NVD entry mirrors the published vulnerability description and score. Its reference list includes a GitHub security advisory, but that advisory was not publicly accessible when we checked. The CVE record, NVD entry, and 0.21.0 release are the available primary sources for the affected range and fix.
- [ CRITICAL ]CVE-2026-120338Prefab UI Generative UI sandbox escape
Found this useful? Share it.