Analysis
The long view — why the pattern keeps repeating, and what it says about the industry.
236 articles · newest first

Cisco Expressway CVE-2026-76466 Exploited After PoC
F6 reports the first in-the-wild exploitation of Cisco Expressway CVE-2026-76466, a root command execution flaw, weeks after a patch and a public PoC.
vCenter Zero-Day CVE-2026-123890 Patched After Exploitation
Broadcom patched a critical vCenter auth bypass, CVE-2026-123890, that Mandiant says a China-linked group exploited since September. Patch and check for compromise.
NVIDIA Probes Gentlemen Ransomware Leak-Site Claim
The Gentlemen ransomware group listed NVIDIA on its leak site with a November 28 countdown. NVIDIA says it found no sign its own systems were hit.
Ukraine and FBI Arrest Four in $40.5M Ransomware Case
Ukrainian police and the FBI arrested four suspects tied to a ransomware organization linked to $40.5 million in payments from at least 28 companies.
Apache Roller RCE CVE-2026-129448 Is Exploited in Attacks
Apache says a Roller XML-RPC deserialization flaw is under active exploitation. Upgrade to 6.1.6 or later; turning XML-RPC off in the admin UI is not enough.
Lithuanian Customs Restores Services After BAP Breach
Lithuania's customs agency confirmed unauthorized access to its BAP portal and a possible data breach affecting users who logged in on November 9-10.
Italy Fines Meta €805M Over Facebook Android Gallery Access
Italy's data protection authority fined Meta €805 million over a default-on Facebook feature that read Android photo galleries without explicit consent.
PTC Patches New Critical Windchill and FlexPLM RCE
CVE-2026-126325 is a deserialization flaw rated CVSS v4 9.2 in Windchill and FlexPLM. PTC-hosted systems are already fixed; self-hosted ones need the patch.
Apache HTTP Server 2.4.71 Fixes Critical mod_http2 RCE
CVE-2026-119618 is a race condition in Apache's mod_http2 that can allow unauthenticated code execution. Upgrade to 2.4.71 or turn off HTTP/2 until you can.
US Agencies Warn of Attacks on Refrigeration Controllers
CISA, FBI, HHS, USDA and DOT say actors are hitting internet-exposed cold-chain controllers, forcing heating and defrost cycles. Here is what operators should do.
OpenEMR advisories cover portal, fax and FHIR flaws
Three OpenEMR advisories describe patient-record exposure through the portal, fax/SMS module and FHIR API. Patched releases are 8.3.0 and 8.4.0.
Kyverno 1.19.1 Namespace Clamp Bypass Reaches Cluster Admin
A critical Kyverno advisory says a namespace tenant can escape the apiCall clamp added in 1.19.1 and escalate to cluster admin. Version 1.19.2 fixes it.
Vikunja 2.7.1 fixes a null-filter crash in project views
A Low-severity Vikunja advisory describes how a project admin could save a malformed view filter that makes every read of that view fail. Version 2.7.1 fixes it.
SonicOS SSL-VPN SAML Bypass Exploited, Patch Now
SonicWall fixed seven SonicOS flaws, including CVE-2026-19868, an SSL-VPN SAML bypass exploited in attacks and on CISA's KEV list. No workaround exists.
D-Link DGS-3130 Switches Have Unpatched DDP Flaws
D-Link disclosed unpatched flaws in DGS-3130 switches involving its Discovery Protocol. No CVE IDs yet. Disable DDP and isolate management access.
SonicWall Won't Patch Two Flaws in End-of-Life GMS
SonicWall says GMS 9.5.2 and earlier has an unauthenticated file read and a SQL injection flaw, and that no fix is coming. Owners are told to move to NSM.
Android November Patches Fix 200+ Flaws, Framework RCE Tops
Google's November Android bulletin fixes more than 200 vulnerabilities across two patch levels, led by a critical zero-click Framework RCE, CVE-2026-58868.
NCSC Expects AI-Driven Attacks on UK Infrastructure by 2028
The UK's cyber chief warned that AI will help criminals and states exploit long-tolerated weaknesses at scale. The NCSC's own report says it mostly sharpens old tactics.
Langflow Critical Flaws Need an Upgrade to 1.13.0
IBM reports two critical unauthenticated Langflow flaws, CVE-2026-93680 and CVE-2026-110186. Every release through 1.12.8 is affected; 1.13.0 is the only fix.
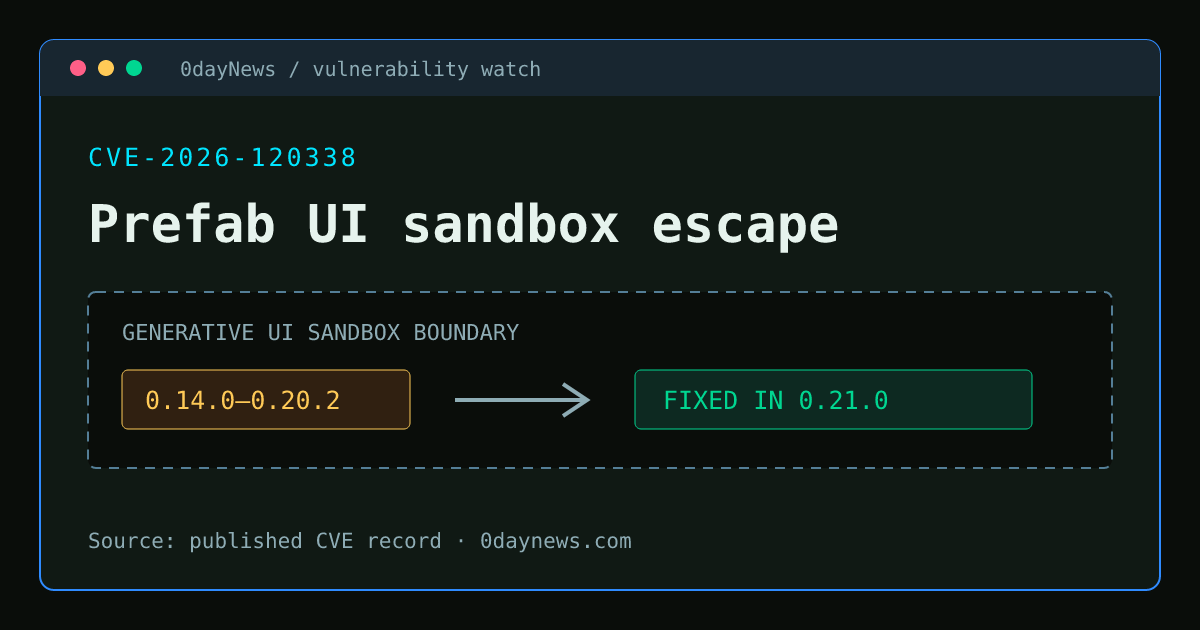
Prefab UI sandbox escape fixed in 0.21.0
CVE-2026-120338 affects Prefab UI's optional Generative UI sandbox in versions 0.14.0 through 0.20.2. The 0.21.0 release contains the fix.