News archive Page 2
918 articles · sorted newest first · page 2 of 39
Looking for a specific story? Search and filter the full archive.
BYOD ransomware gang claims Michigan State data theft
BYOD listed Michigan State University on its leak site, claiming data on 1.3 million people. The school ties it to an October credential incident and disputes wider access.
Android November Patches Fix 200+ Flaws, Framework RCE Tops
Google's November Android bulletin fixes more than 200 vulnerabilities across two patch levels, led by a critical zero-click Framework RCE, CVE-2026-58868.
Barracuda Patches Chainable Flaws Giving Root Access
Barracuda fixed CVE-2026-116606 and CVE-2026-111560, which together can bypass authorization and yield root. Restrict admin interfaces and patch now.
3AM Ransomware Hits UK School Estate, AI Use Suspected
Bitdefender documents a 3AM ransomware affiliate encrypting about 37 machines in a UK school estate. Command timing suggests automation. Confidence: low to moderate.
NCSC Expects AI-Driven Attacks on UK Infrastructure by 2028
The UK's cyber chief warned that AI will help criminals and states exploit long-tolerated weaknesses at scale. The NCSC's own report says it mostly sharpens old tactics.
Siemens IoT2050 Node-RED Flaw Exploited by Botnet
VulnCheck saw attacks on CVE-2026-58115, a CVSS 10.0 Node-RED flaw on Siemens SIMATIC IoT2050 Advanced. Siemens fixed it in August. Here is what to do.
Synology Warns of C3RB3R Ransomware Hitting Old DSM
Synology says attackers are exploiting a DSM flaw patched in December 2024 to encrypt NAS data with C3RB3R ransomware. The vendor names no CVE.
BTCPay Server Hot Wallets Drained on Outdated Instances
BTCPay Server's maintainer reports hot wallet thefts on instances running 2.4.1 or older. No credible drains reported on 2.4.7. Investigation is ongoing.
Langflow Critical Flaws Need an Upgrade to 1.13.0
IBM reports two critical unauthenticated Langflow flaws, CVE-2026-93680 and CVE-2026-110186. Every release through 1.12.8 is affected; 1.13.0 is the only fix.
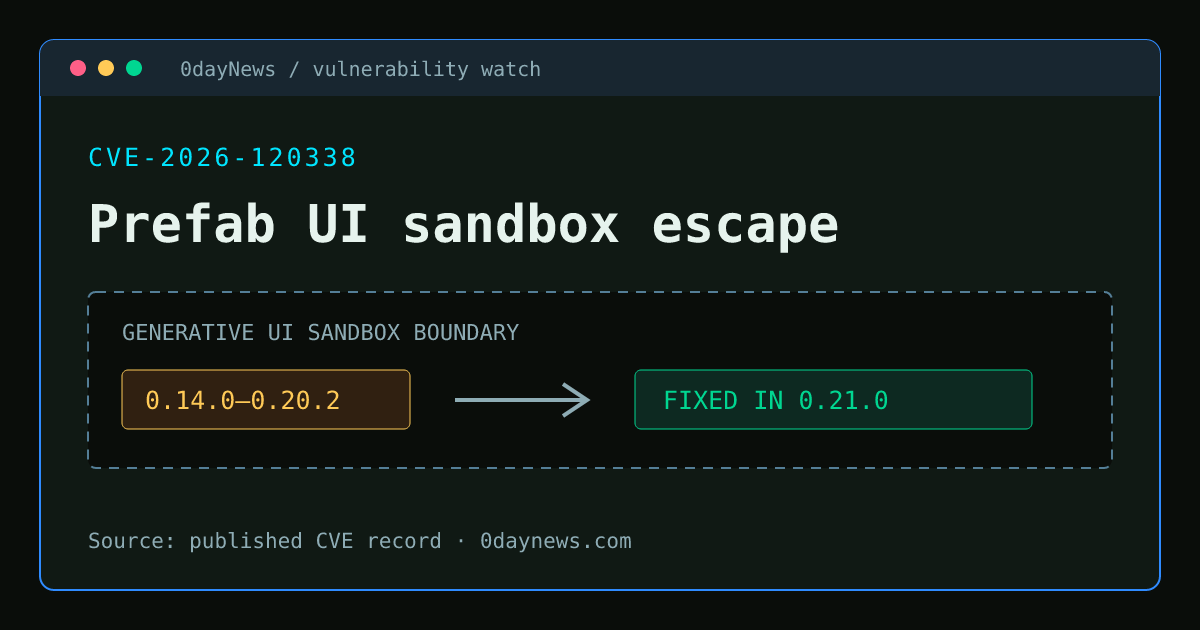
Prefab UI sandbox escape fixed in 0.21.0
CVE-2026-120338 affects Prefab UI's optional Generative UI sandbox in versions 0.14.0 through 0.20.2. The 0.21.0 release contains the fix.
Three Command Injection CVEs Affect WAVLINK WN553X1-B
Three published CVE records identify command injection flaws in WAVLINK WN553X1-B firmware. All carry a CNA CVSS 3.1 score of 9.9.
Android 'SMS of Death' Crash Fix Exists, but Patch Coverage Is Unclear
Google's Android source contains a fix for a remote telephony crash. The October bulletin does not identify the issue, so device patch coverage remains unconfirmed.
Chainalysis Confirms Breach by 'Agentic' Attacker
Chainalysis confirms an external actor reached internal tools and customer contact data using 'offensive agentic techniques'. Entry point and dwell time unconfirmed.
Ivanti Connect Secure Chain Fixes Ship, KEV Due Nov 2
CISA added Ivanti Connect Secure CVE-2026-111357 and CVE-2026-118527 to KEV. Fixes for the full exploited chain are now out in 25.1.1.3 and 22.8R2.6.
FBI Seizes Virtualine Bulletproof Hosting Domain
The FBI seized virtualine.net, a Russian-speaking bulletproof host tied to ransomware and StealC operators. A domain seizure alone does not prove it is offline.
Linux TCP Flaw Allows Remote Root on MPTCP Listeners
Anthropic demonstrated remote root execution through Linux CVE-2026-98432 on MPTCP listeners. Upstream fixes exist; distribution patch status varies.
Drupal Commerce Core Bypass Exploited, Patch 3.3.13
Drupal says CVE-2026-118539, a highly critical Commerce Core access bypass, is exploited in the wild. Update to 3.3.13 or 8.x-2.41 and audit your orders.
GitLab CVE-2026-97229 Hit Alpine Linux, Now in KEV
CISA added GitLab's CVSS 10.0 RCE to KEV after an attempted attack on Alpine Linux's instance. Federal deadline is Nov 1. Patch, then check for crashes.
Low-Severity ESXi Logging Flaw Hits CISA KEV
CISA added VMware ESXi CVE-2026-41709, a CVSS 2.7 logging flaw, to KEV after CrowdStrike tied it to Warp Panda zero-day use. Patch and review ESXi audit gaps.
Cisco Patches ASA/FTD VPN Zero-Day, Active Attacks
CVE-2026-76418 lets unauthenticated attackers crash Cisco ASA and FTD firewalls via SSL VPN. Cisco confirmed active exploitation; patches released October 29.
Ukrainian Hive and Nefilim Affiliate Gets 70 Months
Artem Stryzhak, 35, sentenced to 70 months for Nefilim and Hive ransomware attacks on hospitals and corporations causing more than $100M in losses.
Adobe Patches 8 Critical Campaign Classic Flaws
Adobe patched eight critical flaws in Campaign Classic 7.4.4 build 9402, including a CVSS 10.0 SQL injection. Build 9403 is available now; no active exploitation reported.
CISA Adds Adobe Commerce, Brotli to KEV After Active Attacks
CISA added CVE-2026-48356 and CVE-2026-111497 to its KEV catalog as PolyShell attacks breach hundreds of Adobe Commerce and Magento stores.
Oracle EBS SQL Injection Probed 24 Hours After Patch
Threat actors began probing Oracle EBS CVE-2026-101767, a CVSS 9.8 unauthenticated SQL injection, one day after Oracle's October 2026 CPU released the fix.