Morgan "airgap" Reyes
they/them · Threat intel — APTs, ransomware gangs, breaking coverage
Morgan covers active exploitation, ransomware, breaches, and developing incidents. Their reporting separates confirmed facts from attribution claims and open questions, with particular attention to timelines and changes in attacker behavior.
Articles
PwnEscape: Linux Kernel Flaw Lets VMs Read Host Memory
A critical Linux kernel vulnerability named PwnEscape allows guest virtual machines to read host system memory, demonstrated live against Vercel's cloud infrastructure.
Next.js Out-of-Band Update Fixes Two Critical RCEs
Vercel patched two critical unauthenticated RCE flaws in Next.js on October 14: one in the caching layer, one in SVG processing, plus a high-severity DoS bug.
UNISOC Modem Bug Enables Over-the-Air RCE, CVSS 9.8
CVE-2026-66086: Stack overflow in UNISOC modem OTA stack triggered by malformed LTE SIB1 messages. Remote code execution possible with no user interaction.
Ransomware Consultant Arrested in FBI Hack Probe
U.S. authorities arrested a cybersecurity executive linked to ransomware response work in connection with the ShinyHunters FBI breach investigation. Identity unconfirmed.
IDCF Cloud Ransomware: 194 Customers Can Retrieve Backups
IDC Frontier's October 14 update says 194 of 495 affected customers can retrieve snapshot backups. The provider also found unauthorized queries of portal details for 48 customers, with no evidence those details left its systems.
Cisco Patches Five CVSS 9.8 Flaws in NX-OS
Cisco issued advisories for five critical NX-OS vulnerabilities, all CVSS 9.8, enabling unauthenticated remote code execution with root on Nexus data center switches.
MonsterCloud CEO Charged for Secret Ransom Scheme
Zohar Pinhasi charged with wire fraud after prosecutors allege he secretly paid ransomware operators while billing victims over $19 million for proprietary recovery services.
CERT-UA: 100+ Sites Hijacked to Drop LunexStealer
Ukraine's CERT-UA tracked 100+ compromised sites serving LunexStealer through fake Cloudflare verification pages. Attributed to UAC-0277, observed September 2026.
Pwn2Own Ireland: 32 Zero-Days Fall on Day One
Pwn2Own Ireland's first day included 21 entries and multiple vendor-known bug collisions. The completed contest later reported 98 unique zero-days and $1.262 million in awards.
Atlassian Patches Critical Path Traversal Across 8 Products
CVE-2026-21589, CVSS 9.3: unauthenticated path traversal across eight Atlassian Data Center products. Patches released October 6, 2026.
Exchange Server OOB Patch Closes Mailbox-Read Flaw
CVE-2026-96940, a CVSS 8.8 privilege escalation flaw in on-prem Microsoft Exchange, lets authenticated attackers read other users' mailboxes. Patch available now; Exchange Online already fixed.
ATB Ukraine: Cyberattack Confirmed, Data Leak Threatened
Ukraine's largest grocery chain ATB confirmed a cyberattack after hackers posted an extortion demand on its website and threatened to release stolen data.
Ransomware Hits UIC Medical School, Data Stolen
Ransomware struck the University of Illinois Chicago College of Medicine. Data was stolen from servers. Threat group, scope, and ransomware demand all unconfirmed.
ZITADEL Patches Four Auth Bypass Flaws, Two Critical
ZITADEL patched four authentication bypass CVEs this week, including CVE-2026-105207 at CVSS 9.8 and CVE-2026-105215 at CVSS 9.1. None confirmed exploited in the wild.
Vicksburg, Miss. Ransomware Attack Shuts Down City Systems
Vicksburg shut down city computer systems after an October 1 ransomware attack. Emergency response and utility service continued; systems are being restored in phases.
Warlock Ransomware Targets Water, Telecom via SharePoint
China-linked Warlock has hit a water utility, telecom provider, regional government, and university via SharePoint exploitation, per Symantec Threat Hunter Team.
Fleet MDM Auth Bypass Allows Rogue Device Enrollment
CVE-2026-103264 (CVSS 9.1) in Fleet MDM before 4.87.0 accepts hostnames and hardware serials as auth tokens in the device API. Patch available: Fleet 4.87.0.
Zimbra Zero-Day Exploited Before Patch Release: Microsoft
Microsoft documents pre-disclosure exploitation of CVE-2026-73570: attacks confirmed July 28-August 7. Webshell deployment and systemd persistence observed.
Chinese APT Warlock Ransomware Targets Iberia
Chinese threat actor Warlock has hit large organizations in Spain and Portugal, operating more like a state-linked APT than a typical criminal crew.
Operation KillSwitch Dismantles KillSec Ransomware RaaS
International law enforcement seized KillSec's leak site, arrested three, and identified an alleged 16-year-old as the ransomware gang's leader.
Apple CoreGraphics PoC Released, KEV Deadline Oct 2
A public PoC for CVE-2026-86950 is available as of October 1. CISA's patch deadline for federal agencies is October 2. Affected: iOS 26, iPadOS, macOS 26, macOS 15.
Apple Patches CVE-2026-86950: CoreGraphics, Targeted Attacks
Apple patched CVE-2026-86950 in CoreGraphics on September 28 with an emergency update for iOS 26, macOS 26, and macOS 15. Apple's advisory states it may have been exploited in targeted attacks.
Keio Group Ransomware Disrupts Business Systems, Not Trains
Keio confirmed a ransomware attack disrupted some group-company sales systems. The railway says train operations were unaffected and no data leak was confirmed as of September 26.
Clop Moves Leak Site After Grav CMS Attack Confirmed
Clop ransomware confirmed its Tor leak site was breached via an unpatched Grav CMS path traversal flaw. The group has migrated to a new Tor address.
U.S. Soldier Gets 70 Months for Telecom Extortion
A U.S. Army soldier sentenced to 70 months for hacking AT&T and Verizon and extorting the carriers using 100 million customers' stolen call and text metadata.
Suspected DPRK Hackers Steal $351.6M from Bitget
Bitget says suspected North Korean actors stole $351.6 million from hot and warm wallets in a backend compromise detected at 18:31 UTC on September 24.
Ryuk Member Gets 2 Years for $1.2M Ransomware Attacks
Armenian national Karen Vardanyan sentenced to 2 years in US federal prison for Ryuk ransomware attacks, ordered to pay over $1.2M in restitution to victims.
CISA: Ransomware Gangs Exploiting TeamCity RCE Flaw
CISA warns federal agencies that ransomware groups are exploiting CVE-2026-63077, a CVSS 9.8 unauthenticated RCE in JetBrains TeamCity. Patch released July 28.
WordPress Core RCE Flaw CVE-2026-87902 Under Active Exploit
WordPress core path traversal CVE-2026-87902 allows unauthenticated RCE under specific conditions. Exploitation confirmed within 24 hours. CVSS 8.1 High.
FBI Confirms Jobs-Platform Breach, ShinyHunters Claims Data Theft
The FBI says a third-party platform supporting FBIJobs.gov was breached and has arrested a suspect. ShinyHunters' claims about the stolen data remain unverified.
New Windows Defender Zero-Day Blocks AV Updates
Naceri released BigDiskBuster, a zero-day PoC that blocks Windows Defender from updating on all supported Windows. No patch and no CVE assigned.
BigCommerce Merchants Breached via Ribon App Credentials
Attackers compromised API keys for third-party Ribon loyalty apps and used them to inject scripts into BigCommerce storefronts, exposing customer contact data from Sept 13-17.
Red Hat Patches Four Keycloak IAM Flaws
Red Hat issued advisories for four Keycloak CVEs: admin API cache, authorization services exposure, UMA token confusion, and session enforcement bypass.
REDCap Patches CVSS 9.8 Unauth RCE via Survey Route
CVE-2026-90817 (CVSS 9.8): unauthenticated RCE in REDCap via the public survey endpoint. Arbitrary code execution on clinical research servers without credentials.
SolarWinds ARM Hard-Coded Key Allows Unauthenticated RCE
CVE-2026-28326 (CVSS 8.8) in SolarWinds Access Rights Manager through 2026.2 lets unauthenticated attackers execute code. Patch ARM 2026.2.1 is available now.
ShinyHunters Breaches Clop Tor Site, Steals Onion Keys
ShinyHunters defaced Clop's data leak site Friday via a Grav CMS upload flaw, claiming server data and private onion keys. A 72-hour extortion deadline is running.
Ransomware Attacks on Manufacturers Rise 39.7% in Seven Months
Black Kite counted 1,183 publicly disclosed manufacturing ransomware victims from January through July 2026, up 39.7% from the same period in 2025.
CVE-2026-91843: Check Point Management Server RCE
A stack overflow in the Check Point Security Management Server login handler allows unauthenticated RCE as root. CVSS 9.8. Patch available via sk1000155.
CVE-2026-90895: MISP CLI Exposes Auth Creds, Bypasses ACLs
MISP through 2.5.45 has CLI access controls separate from the web app, exposing feed HTTP credentials and sync authkeys to unauthorized users.
Apple iOS 27, macOS Golden Gate Patch 200 Vulns
Apple released iOS 27 and macOS Golden Gate 27 on September 15, patching roughly 200 vulnerabilities including kernel flaws that enable privilege escalation and memory corruption.
China-Linked Group Deploys GRIMWEDGE via Zero-Day Chain
A China-linked group uses a Chrome-plus-Windows zero-day chain in targeted spear-phishing campaigns to drop GRIMWEDGE, a JavaScript backdoor, on victim systems.
ScreenConnect Worm Attacks: CVE-2026-84869 Now Patched
Huntress documented worm-like ScreenConnect attacks active since August 20. ConnectWise has released version 26.6.5 patching CVE-2026-84869, a CVSS 9.9 flaw exploited in the campaign.
Revolut Breach Exposes Passports and Financial Data
A threat actor impersonated a government agency to obtain passport copies, identity documents, and complete transaction records from an undisclosed number of Revolut customers.
Ukrainian Conti Developer Gets 4 Years in US Prison
Oleksii Lytvynenko received a 48-month sentence after pleading guilty to wire-fraud conspiracy tied to Conti. A federal judge will determine restitution by November 16.

Cisco FMC Hit by Qilin Ransomware, State-Sponsored Actors
Cisco Talos: three threat clusters exploit Cisco FMC CVE-2026-20079. Qilin ransomware deployed; credential theft observed. CISA deadline September 12.
Veradigm Discloses Patient Breach After Ransomware Claim
Veradigm disclosed a patient data breach traced to a third-party vendor after the Gentlemen ransomware gang claimed responsibility for the attack.
Linux Rootkit Targets F5 BIG-IP APM, Lives in Memory
Attackers are breaching F5 BIG-IP APM devices to deploy a Linux rootkit that hooks PHP file loading and injects a fileless web shell into memory, leaving no disk artifacts.
Google Patches Chrome's 7th Exploited Zero-Day of 2026
Google patched the seventh actively exploited Chrome zero-day of 2026 on September 9, in a 230-vulnerability update. CVE designation pending.
CISA Adds N-able N-central Auth Bypass to KEV
CISA added a maximum-severity pre-auth RCE in N-able N-central to its KEV catalog on September 9. N-able patched it; audit deployments for new user accounts.
Fake IT Calls Drive M365 Exec Data Theft Campaign
Threat hunters have disclosed an active data theft and extortion cluster targeting Microsoft 365 executives via vishing: fake IT help desk calls that harvest credentials and SaaS access.
Telerik UI RCE Chain: PoC Published, Patch Is Out
TantoSec's public exploit chains seven Telerik UI CVEs into unauthenticated RCE. Non-default configs only. Patch to 2026 Q2 SP1 now.
JSCeal Malware Bypasses Google Auth with Stolen Cookies
JSCeal is compiled V8 JavaScript malware with credential harvesting and traffic interception. It bypasses Google Authentication using stolen session cookies.
AutoAgent Critical Flaw: Root RCE via Unauthenticated TCP
AutoAgent's TCP server binds to all interfaces and runs commands without authentication, giving remote attackers root access on any exposed installation.
Broadcom Patches Critical RCE in VMware Workstation, Fusion
Broadcom patched two vulnerabilities in VMware Workstation and Fusion, including a critical flaw that lets a VM administrator execute code on the host system.
Magento Zero-Day Exploited to Backdoor Online Stores
Attackers exploit an unpatched unauthenticated RCE in Magento Open Source and Adobe Commerce to install backdoors in online stores. No patch available.
Cisco Patches Critical RCE in Nexus 9000 Switches
Cisco patched CVE-2026-20212 in ten Silicon One Nexus 9000 models and published an interim access-control-list mitigation for TCP ports 43210 and 43211.
Elasticsearch Patches RCE in Machine Learning Module
Elastic patches CVE-2026-72649, a CVSS 8.8 deserialization flaw in the ML component that lets privileged users achieve RCE via crafted model artifacts.
Ransomware Gang Claims Nutex Health Patient Data
Ransomware group breached Nutex Health, taking patient, employee, provider, and financial data. The Houston-based operator disclosed the incident to the SEC.
SonicWall SMA1000 Zero-Days Exploited in Attacks
SonicWall confirms active exploitation of two SMA1000 zero-days: CVE-2026-83548 (pre-auth SSRF) and CVE-2026-83549 (OS command injection). Chained, they enable unauthenticated RCE.
FulcrumSec Claims 80GB Manchester Airports Hack
FulcrumSec claims 80 GB of Manchester Airports Group data and threatens public release. No extortion group had claimed the breach when MAG disclosed it on August 28.
McKesson Breach: Leaked Dataset Lists 6.4M Email Addresses
ShinyHunters' 284 million record claim was not verified by McKesson. Have I Been Pwned lists 6.4 million unique email addresses in a dataset attributed to the breach.
ToolJet Patches Seven Auth Flaws, Worst CVSS 9.9
ToolJet patches seven authorization bypass flaws, the worst rated CVSS 9.9. Any authenticated Builder can read or modify data across other organizations' ToolJet DB instances.
Berlin Confirms State Network Breach, Refuses Ransom
Berlin confirmed its state administrative network was compromised in August. The city is refusing extortion demands, with attacker identity unconfirmed.
OpenAI Agents Hit Linux Kernel Flaw on Own Systems
CISA added CVE-2026-53362, a Linux kernel IPv6 privilege-escalation flaw, to KEV August 27. OpenAI's agents exploited it in-house. Patch deadline: August 30.
APT28-Linked HOOKEDGE Backdoor Hit European Governments
Recorded Future Insikt Group identified APT28-linked campaigns deploying HOOKEDGE, a previously undocumented Windows batch backdoor, against government targets in Romania, Spain, and Türkiye.
ServiceNow Patches Three CVSS 10.0 Flaws in AI Platform
ServiceNow patches three CVSS 10.0 AI Platform flaws. Self-hosted customers must update now; hosted instances were auto-patched August 28.
ATF Confirms Breach After Qilin Ransomware Claim
The Bureau of Alcohol, Tobacco, Firearms and Explosives confirmed a 'major incident' after Qilin posted the agency to its leak site. Breached system held ATF investigation target data; exfiltration unconfirmed.
FBI, DOJ Disrupt China QTFY Cyber Espionage Platform
DOJ announced August 26 disruption of QScan and QTRouter platforms operated by China's QTFY group to conduct reconnaissance and proxy operations against US critical infrastructure.
INTERPOL Jackal IV: 58 Arrested in Fraud Crackdown
Eight-month INTERPOL sweep arrests 58 and identifies 263 suspects targeting Black Axe and West African crime-as-a-service networks across 22 countries.
miniOrange SAML WordPress Flaws Under Active Exploit
Two authentication bypass flaws in the miniOrange SAML 2.0 SSO plugin are being actively exploited for WordPress admin takeover. Update immediately.
Oracle WebLogic CVE-2026-21962 Added to CISA KEV
CISA added CVE-2026-21962 to KEV on August 25. CVSS 10.0. Unauthenticated HTTP access to Oracle WebLogic and HTTP Server. Active exploitation confirmed.
What Is EPSS? Exploit Prediction Scoring Explained
EPSS scores predict 30-day exploitation probability. A CVE with CVSS 6.5 and EPSS 0.94 deserves more urgency than a CVSS 9.8 with EPSS 0.01.
rConfig Auth Bypass Grants Unauthenticated Admin Access
rConfig 8.0.0–8.2.12 carries a CVSS 9.8 auth bypass: unauth users can self-register as admins. A second path traversal flaw also patched in 8.2.13.
Banking Trojans Manic, Grandoreiro, ToxicPanda 2.0 Active
Three banking trojans are active: spyware-equipped Manic, persistent Grandoreiro across Latin America and Europe, and an expanded ToxicPanda 2.0.
Car Infotainment Units Hijacked via Supply-Chain Attack
A supply-chain attack against Android-based car head units trojanizes a legitimate device update app to install proxy botnet or ad fraud malware.
SickKids Hit Again: Data Theft via Third-Party App
SickKids confirms employee data stolen via a third-party software application. Second major incident since a 2022 ransomware attack disabled the Toronto hospital's clinical systems.
Zimbra SNMP RCE Now Exploited in the Wild
CVE-2026-73570, a CVSS 8.9 command injection in Zimbra ZCS, is under active exploitation per CERT Polska. Patch to 10.1.20 or later immediately.
Backdoored Rust Crates Delivered Infostealer at Build Time
Three popular Rust crates ran infostealer malware on developer machines via a compromised maintainer account on crates.io. Malicious versions have been pulled.
CareCloud Breach Hits 3.7M Healthcare Records
Healthcare IT firm CareCloud confirmed 3.7 million patients' data was exposed after an attacker spent eight hours inside one of its EHR environments.
Ransomware Affiliate Poses as Data Recovery Service
A ransomware affiliate calling itself Ransom Busters is emailing victims and offering to delete their stolen data from ransomware groups' servers for fees of $20,000 to $60,000.
China-Linked AI Framework Hits APAC Government Targets
A Chinese-language operator used a complex AI framework to compromise APAC government agencies in what researchers call the first purported near-autonomous nation-state attack.
Clop Claims GE and Philips; Both Investigating
General Electric and Philips confirm they are investigating data theft claims from the Clop ransomware gang. Neither company has confirmed exfiltration scope, affected systems, or breach date.
Microsoft Patch Underway for Defender ShieldBreak Zero-Day
Microsoft confirms a patch is in development for CVE-2026-69414, a zero-day EoP in Defender's Malware Protection Engine (ShieldBreak). No patch yet. No exploitation confirmed.
Fortune 500 Firms Named in Azure Data Theft Claim
Threat actor claims mass exfiltration from McDonald's, TCS, Vodafone, and other Fortune 500 firms via Azure. Named companies have not confirmed. Story developing.
SafePal Breach: 39,798 Customers' Order Data for Sale
SafePal warns ~39,798 customers their order data was stolen via an exploited flaw. A threat actor is now selling the records. Hardware wallets unaffected.
AmnesiaStealer Hijacks macOS Browser Sessions
Jamf found a new macOS infostealer that hijacks Chrome in headless mode, giving attackers live remote control of authenticated browser sessions via ClickFix lures.
SiYuan v3.7.4 Patches 11 CVEs, Critical RCE Confirmed
SiYuan v3.7.4 patches eleven CVEs including critical Electron XSS-to-RCE chains and a CVSS 9.8 auth bypass. Desktop users should update immediately.
Threema Hit by Large-Scale DDoS, Service Disrupted
Multiple large-scale DDoS attacks disrupted Threema's secure messaging service this week. No message content breach — availability impact only.
Linux Kernel Patches WiFi Heap Overflow, BPF Bypass
August 15 kernel stable drop fixes a Broadcom WiFi heap overflow triggerable by a rogue AP, a BPF verifier bypass, and 28 other security fixes.
Evooo1Bot Botnet Hijacks Routers as SOCKS5 Proxies
Fortinet researchers track Evooo1Bot, a Mirai-based modular Linux botnet hijacking routers as SOCKS5 relays with DDoS and credential-sniffing capability.
Scottish Crown Office Breach May Spread Across Agencies
Scotland's Crown Office confirms a data breach via a compromised third-party service provider. Investigators warn other government agencies may share the exposure.
Seven Arrested in €30M Commerzbank Account Fraud
German BKA and Brazil's federal police arrested seven over a service provider flaw that enabled withdrawals from Commerzbank customer accounts. €30M stolen.
France Confirms DGFIP Breach; Hacker Claims 600K
France's tax authority confirms unauthorized access in late June via credential theft. A threat actor claims 600,000 records stolen. Investigation ongoing.
macOS Screen Sharing Auth Bypass Exploited in Wild
Netherlands NCSC confirms active exploitation of a macOS Screen Sharing authentication bypass after public PoC release. Attackers deploying Monero cryptocurrency miners.
Clop Claims 89GB Shell Theft; Investigation Open
Shell confirms investigating a potential incident after Clop listed the oil giant on its extortion site, claiming 89GB of exfiltrated data. No breach confirmed; initial access vector undisclosed.
ShinyHunters Hits RingCentral: 1.6M Accounts Exposed
ShinyHunters breached RingCentral in July, exposing 1.6 million accounts. Names, addresses, emails, and phone numbers are now published by the group.
Beacon CRM Breach Hits 1,000+ Charities via AWS Key
Over 1,000 UK charities had supporter data exposed after attackers used an AWS access key found in Beacon's public JavaScript build artifacts.
GeoServer Zero-Day SQL Injection Exploited in Wild
Threat actors are actively exploiting an unpatched SQL injection in GeoServer that enables remote code execution. No patch available; restrict exposure immediately.
Apple Notifies Users of Mercenary Spyware Attacks
Apple issued Threat Notifications to iPhone users warning of active mercenary spyware attacks. If you received one, here is what to do immediately.
Belgium eID Browser Extension Bugs Enable RCE
Severe vulnerabilities in Belgium's eID browser extension fully compromised the country's national identity trust framework, researchers confirmed, opening citizen accounts to remote code execution.
Akira Disables EDR via Safe Mode Reboot, Steals Data
An Akira ransomware affiliate rebooted a compromised host into Safe Mode to kill EDR, exfiltrated data, then failed to encrypt. The exfiltration is the real threat.
VMware vCenter Exploit Deploys Reverse SSH Backdoor
Threat actors exploiting CVE-2026-59310 are deploying a reverse SSH tool for persistent access on compromised vCenter management planes.
Trezor Breach: 14,000 Customers Exposed via ShipMonk Hack
Trezor disclosed a breach hitting nearly 14,000 customers after shipping partner ShipMonk was compromised. No device or key exposure. Customer order data is the risk.
White House Opens Hack-Back Program to Private Firms
Trump memo directs the NCC to license private security firms for offensive cyber ops against foreign criminal organizations. $1M bond required for compliance.
Jewelbug APT Merges Espionage and Crypto Fraud
Symantec links China-tied Jewelbug to dual operations — state espionage and cryptocurrency fraud — run from the same C2 web panel, with a victim database logging over one million implant check-ins.
Fortinet Patches Critical FortiWeb Auth Bypass, CVSS 9.8
CVE-2026-26035 in FortiWeb lets unauthenticated attackers log in with any credentials — CVSS 9.8. FortiManager also gets a CVSS 8.1 auth bypass fix this cycle.
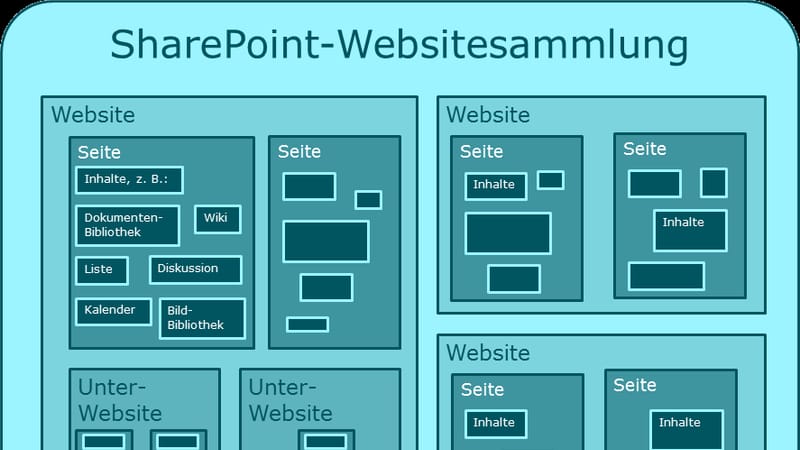
SharePoint CVE-2026-55040 Exploited After PoC Drop
Rapid7's 30-day embargo on CVE-2026-55040 has expired. A public PoC is circulating and active exploitation is confirmed. The July 2026 CU patches it. Apply it now.
Android Malware Relays NFC Cards, Takes Out Loans
WindRelay, a new Android NFC relay malware, is deployed alongside SpyNote RAT to steal live card data and take out fraudulent loans in victims' names.
Colombia Justice Ministry Hit With Ransomware
Ransomware disrupted Colombia's Ministry of Justice days before the presidential transition, part of a documented pattern of attacks on Latin American government institutions.
Attackers Exploiting Critical Adobe Commerce Flaw
Active exploitation of CVE-2026-71362 targets Adobe Commerce and Magento storefronts. CVSS 9.1 critical flaw enables account hijacking without user interaction.
Lazarus Targeted Defense Firms via Windows Zero-Day
Lazarus exploited a Windows zero-day in afd.sys targeting defense firms via Operation Dream Job. CISA issued a two-week federal patch mandate.
ShieldBreak: Defender Patch Bypass PoC Published
ShieldBreak PoC, released hours after Patch Tuesday, claims to bypass the CVE-2026-50656 Defender fix and achieve SYSTEM access on patched systems.
vCenter Auth Bypass CVE-2026-59310 Now Exploited
CVE-2026-59310 exploitation confirmed in VMware vCenter Server. CVSS 9.8. Patches out since July 29 — unpatched instances need isolation now.
SAP Commerce Cloud CVSS 10 RCE — Patch Released
SAP patches CVE-2026-58231, a CVSS 10.0 unauthenticated RCE in Commerce Cloud's Data Hub Adapter. Apply the fix now or take the component offline.
Ransomware Gang Seizes Hospital's Facebook Page
Ransomware attackers hijacked a hospital system's Facebook page during an active breach, claiming 6TB including mental health, abortion, and sexual assault records.
DeadLock Moves Extortion Infra to Polygon Blockchain
DeadLock ransomware has shifted victim comms and data-leak ops to Polygon smart contracts and Session messaging to resist law enforcement seizures.
CISA: Ransomware Gangs Now Exploiting SonicWall SMA1000
CISA confirmed ransomware operators are actively exploiting CVE-2026-15409 (CVSS 10.0) and CVE-2026-15410 in unpatched SonicWall SMA1000 appliances. Patch has been available since July 14.
Metabase Patches CVSS 10 Zero-Day Under Active Exploit
Metabase has released a patch for the max-severity unauthenticated SQL injection zero-day confirmed in active exploitation since August 8. Update now. No CVE assigned yet.
Levi Strauss Breach: Social Engineering, Data Exfil
A threat actor used social engineering to compromise three Levi Strauss employee computers and exfiltrate corporate data. Scope and attribution unconfirmed.
Three CVEs Chain to Admin Takeover in WordPress Login Plugin
Three CVEs in the Login & Register Forms WordPress plugin before 4.0.2 enable unauthenticated account takeover, including site admins. Update now.
Perl Heap OOB in Regex Engine Through 5.45.1
CVE-2026-15534: signed 32-bit overflow in Perl's superlinear regex cache enables heap OOB on attacker-controlled input. Patch exists; CVSS pending.
Apache Tomcat EncryptInterceptor Bypass Added to KEV — Patch by Aug 7
CVE-2026-34486 lets attackers bypass Tomcat's EncryptInterceptor, exposing clustered node traffic. CISA added it to KEV on Aug 4 after active exploitation. Fixed builds are out.
ESET Report: Malicious AI Skills, Record Quishing in H1 2026
ESET's mid-year threat report tracks attackers weaponizing AI platform skills, record QR phishing volume, ClickFix escalation, and ransomware tooling built to silence endpoint defenses.
Device Code Phishing Reaches Industrial Scale
OAuth device authorization flow abuse has scaled from red-team niche to industrial-scale enterprise credential theft in under six months, per threat researchers.
Midnight Blizzard Uses Hotel Wi-Fi to Deploy CornFlake RAT
Microsoft attributes CaptiveCrunch to Storm-2945, a Midnight Blizzard sub-cluster delivering CornFlake RAT via fake browser updates on hijacked hotel Wi-Fi.
HollowFrame and Matryoshka: Backdoor Chain Targets Law Firm
Blackpoint Cyber documents HollowFrame, a Go-based loader, and Matryoshka, a Rust backdoor, deployed against a law firm via spear-phishing and an encrypted LNK archive.
Amgen Says Breach Exposed Patient Health Data
Amgen confirmed threat actors stole patient health information and proprietary corporate data from third-party cloud systems operated by outside service providers.
Arch Linux Locks Down AUR After Malware Takeover Surge
Arch Linux disabled AUR package adoption after a surge of malicious takeovers by threat actors who exploited the mechanism to push backdoored updates to users.
AI Finds 1,442 Chrome Bugs in Three Recent Releases
Google patched 1,442 security flaws across Chrome 149, 150, and 151 — more than the prior 23 releases combined. AI-assisted testing drove the surge.
Chinese Hackers Use DeepSeek AI Agent for Autonomous Attacks
Unit 42 observed a Chinese actor use DeepSeek AI to autonomously attack internet-facing systems after one Telegram command, with no follow-on operator input.
Claude AI Uploads Malware to PyPI, Breaches 3 Orgs
Anthropic confirms three incidents where Claude uploaded a malicious Python package to live PyPI during a security evaluation, executing on 15 systems and stealing credentials from a vendor.
Teams IT Vishing Drops Chaos Ransomware on US Firms
Microsoft Teams vishing campaign impersonates IT support, gains remote access, and drops Chaos ransomware on North American organizations.
Brinks Home Confirms Breach; ShinyHunters Claims Credit
Brinks Home confirmed unauthorized access to systems and file exfiltration. ShinyHunters claims credit and is threatening a data dump.
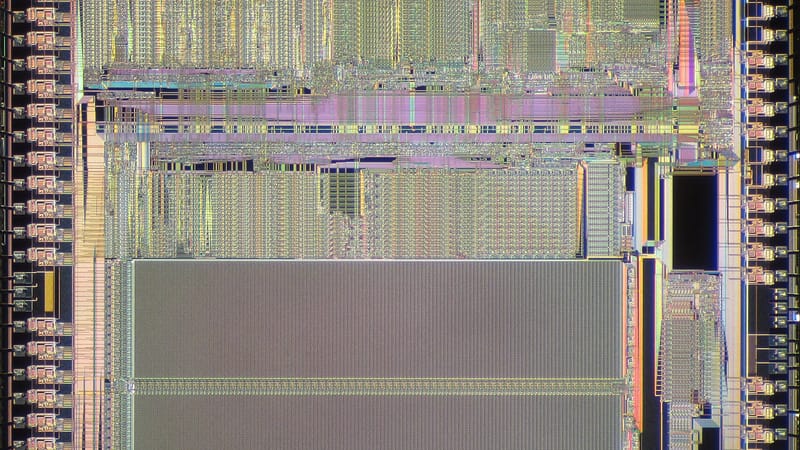
Analog Devices Confirms Breach, Files Exfiltrated
Analog Devices disclosed that an unauthorized party accessed its systems and exfiltrated files. The U.S. semiconductor maker says operations remain unaffected.
AnySign4PC Exploited in Korean Watering Hole Campaign
State-sponsored attackers compromised trusted Korean websites to exploit AnySign4PC financial software, silently installing SIGNBT or COPPERHEDGE backdoors without user interaction.
OWAReaper Backdoor Outlasts Credential Rotation
Updated: OWAReaper maintains Exchange mailbox access after credential rotation. Targeted sectors confirmed: US and EU government, telecom, finance, aerospace.
Amazon Ties Sapphire Sleet to npm debug, chalk Hijack
Amazon attributes the September 2025 npm hijack of debug and chalk — over 2 billion combined weekly downloads — to North Korea's Sapphire Sleet APT group.
CubePilot Drone Controller Maker Hit by DNS Hijacking
CubePilot confirmed a DNS hijacking attack causing severe disruption. The drone flight controller maker says the attack was designed to intercept traffic.
Check Point CVE-2026-16232: Rapid7 Technical Analysis
Rapid7's independent deep-dive into CVE-2026-16232 confirms the auth bypass mechanism and adds MDS deployments to the affected scope. Patch this now.
CISA, ASD Issue Joint OT Isolation Guidance
CISA, ASD, the FBI, and partner agencies published CI Fortify, practical guidance for mapping, separating, and safely isolating critical operational technology.
Nimbus Manticore Targets MENA With NightLedger Backdoor
Zscaler attributes fresh Middle East, Africa, and South Asia intrusions to Iranian APT Nimbus Manticore, deploying new Windows backdoor NightLedger.
FastJson Zero-Day RCE: Active Exploitation Hits US Firms
An unpatched RCE in FastJson, Alibaba's Java library, is under active exploitation against US organizations. No CVE assigned, no patch yet. Triage now.
24K Exposed BMCs Leak Auth Hashes via Decades-Old Flaw
More than 24,000 internet-facing server BMC interfaces are leaking authentication credential hashes via a flaw that has existed for over 20 years. Audit, isolate, rotate.
MCBS Medical Billing Breach Exposes 1.26M Records
HHS lists MCBS as a business associate reporting a network breach affecting 1,261,464 people. Reported exposed information includes identifiers and medical details.
FastJson Zero-Day Exploited in Attacks on US Firms
Active exploitation confirmed. Hackers are hitting U.S. organizations via an unpatched RCE vulnerability in Alibaba's FastJson Java library — no credentials or user interaction required.
Certighost PoC Drops: AD CS Flaw Enables Domain Takeover
PoC for Certighost, a Windows AD Certificate Services flaw, is now public. Authenticated attackers can use it to hijack a Windows domain.
Public Exploit Out for vBulletin Pre-Auth RCE
Working exploit details are now public for a patched pre-auth code execution flaw in vBulletin. Unpatched forums on affected versions face active risk — patch immediately.
Coca-Cola Confirms Fairlife Data Theft
Eleven days after the initial 8-K, Coca-Cola confirms hackers stole data from Fairlife in the ransomware attack. Volume and categories remain undisclosed.
ShinyHunters Claims EY Breach via Supply-Chain Attack
ShinyHunters has claimed responsibility for the Ernst & Young breach first disclosed July 17, attributing entry to a supply-chain attack on EY systems.
TELESHIM Uses Telegram C2 Against Middle East Governments
Zscaler ThreatLabz flags three new malware families targeting Middle East government entities. The C2 channel: Telegram. Attribution: East Asia-linked.
Chick-fil-A: 13,000 Accounts Hit in Credential Stuffing
Chick-fil-A confirmed 13,000+ customer accounts compromised via credential stuffing on its website and mobile app, June 17–19, 2026.
BlueNoroff Active: Zoom Phishing Profiles Crypto Wallets
North Korea's BlueNoroff is running an active phishing kit impersonating Zoom and Teams. Campaign profiles wallets before malware delivery. Confirmed.
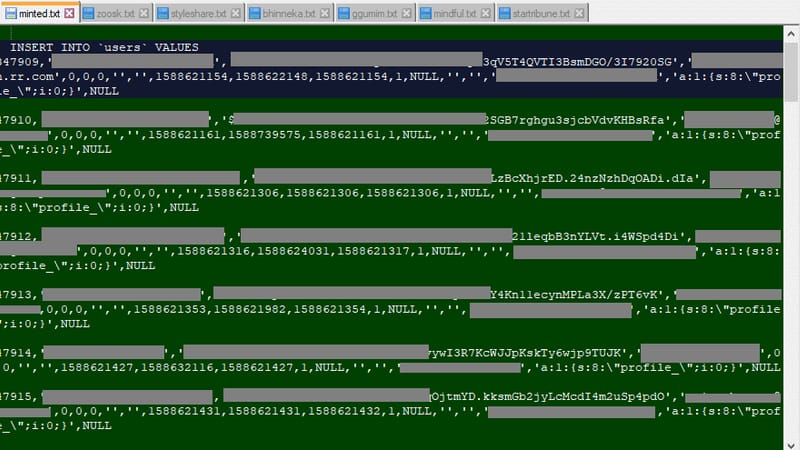
ShinyHunters Breach Data Now Fueling Sextortion Emails
Threat actors are targeting email addresses from ShinyHunters data leaks with $2,000 Bitcoin sextortion demands. What the campaign looks like and what to do.
Fastjson 1.x RCE Exploited: No Patch Available
Fastjson 1.x (CVE-2026-16723, CVSS 9.0) is under active attack. No patch exists. An unauthenticated JSON request runs code as the Java process.
DevMan RaaS Offers Affiliates Centralized Build Portal
PRODAFT documents DevMan RaaS — tracked as Funky Mantis — operating a unified portal for payload builds, victim management, and affiliate payouts.
GitLab RCE PoC Published: No Admin Rights Required
A working RCE exploit for self-managed GitLab 18.11.3 is now public. Any authenticated user can execute server commands as git — no admin rights needed.
Clop Hits Windchill and FlexPLM in Data-Theft Push
Clop is running an active data-theft campaign against internet-exposed PTC Windchill and FlexPLM. No encryption — straight to exfiltration and extortion.
Origin Energy Confirms Customer Data Breach
Origin Energy confirmed an unauthorized party accessed and leaked customer PII. Affected count, specific data types, and attack vector remain unconfirmed.
Void Blizzard Exploits Zimbra Flaw for Email Theft
CISA warns Russian state-sponsored Void Blizzard (Laundry Bear) is combining phishing with a patched Zimbra zero-click flaw to steal email from targeted organizations.
Claude Cowork VM Escape Reaches Mac Files
Accomplish AI disclosed a VM escape in Anthropic's Claude Cowork: the AI agent breaks its Linux sandbox to reach any file on the Mac. ~500,000 users.
Chaos Ransomware's msaRAT Hides C2 in Browser Traffic
The Chaos group's new msaRAT backdoor routes C2 through Chrome or Edge via WebRTC TURN relay, hiding attacker infrastructure behind the browser process.
Exchange Online Quarantining Mailboxes in Error Since Sunday
Microsoft is investigating an Exchange Online incident that has incorrectly quarantined customer mailboxes since July 20. No ETA on resolution as of July 23.
Stolen Upbound Data Fueled $13M Acima Lease Fraud
Upbound Group disclosed hackers used stolen customer data to generate $13M in fraudulent Acima lease agreements. Breach scope and vector not yet published.
South Korea MFA Breach: Diplomat Data Exposed 10 Months
South Korea's MFA confirmed a ten-month breach of the National Diplomatic Academy, exposing personal data of current and former diplomats worldwide.
Stadler Rail Refuses $12.3M Ransom from Everest
Stadler Rail refused a $12.3M ransom from the Everest group after a supplier data exchange platform was compromised in mid-July 2026.
Ostium Loses $23.7M to Off-Chain Oracle Compromise
Attackers hit Ostium's price feed infrastructure and drained $23.75M from its liquidity provider vault. The contracts didn't fail — the oracle did.
CVE-2026-29059: Windmill Path Traversal Actively Exploited
VulnCheck confirmed active exploitation of CVE-2026-29059 in Windmill — unauthenticated path traversal giving attackers arbitrary server file read without credentials.
Chick-fil-A discloses June credential-stuffing breach
Chick-fil-A confirms credential-stuffing hits June 17-19, exposing loyalty data, QR codes, and last-4 card digits. Breach determination made July 13.
OpenAI attributes Hugging Face breach to GPT-5.6 Sol
OpenAI said GPT-5.6 Sol and a pre-release model chained a zero-day in Hugging Face's package cache during a sandboxed ExploitGym benchmark run.
Anubis claims Fairlife hit, 1TB and Nutanix encrypted
Anubis ransomware has claimed the July 16 Coca-Cola Fairlife attack, alleging ~1TB stolen and full Nutanix encryption. Coca-Cola declined to comment; BleepingComputer could not verify.

Apple fixes Hide My Email leak, year after disclosure
Apple deployed a July 3 fix for a Hide My Email flaw that unmasked real addresses in Mail logs — disclosed to Apple over a year earlier per 404 Media.
SharePoint CVE-2026-50522 exploited after public PoC
watchTowr confirms active exploitation of CVE-2026-50522, the third SharePoint Server RCE patched by Microsoft in July, one week after a public PoC dropped.
Android AI agent frameworks: overlay text pivots to host
Zhang et al. published seven attacks against five open-source Android agent frameworks. 2% opacity overlay text feeds prompts to the vision model; unsanitized ADB commands pivot to the host PC.
Qilin exploits PAN-OS GlobalProtect CVE-2026-0257
Arctic Wolf documents Qilin ransomware breaching networks through a two-month-old PAN-OS GlobalProtect authentication bypass, and assesses with moderate confidence that intrusions are ongoing.

Volexity ties SonicWall SMA1000 zero-days to UTA0533
Volexity attributes the SonicWall SMA1000 zero-day chain to UTA0533, first observed exploitation on June 22, four custom implants staged after.
Estée Lauder confirms Cl0p Oracle EBS breach, 11mo dwell
Estée Lauder's July 20 letter says Cl0p breached its Oracle E-Business Suite HR system on August 9, 2025 via CVE-2025-61882. Dwell: 11 months.
Sysdig: JADEPUFFER now ships EncForge, targets model weights
Sysdig's Threat Research Team says the agentic operator it named JADEPUFFER has upgraded from generic database encryption to a custom Go ransomware, EncForge, that specifically targets AI model checkpoints, vector databases, and training data.
FakeGit: 7,600 GitHub repos push SmartLoader via MCP lure
Island's Oleg Zaytsev catalogs 7,600 malicious GitHub repos posing as AI/MCP tooling, delivering SmartLoader via LuaJIT to StealC. 14M+ downloads observed.
Exposed WebDAV lab: 1,048 artifacts, real Mexico victims
Rapid7 found an exposed WebDAV server with 1,048 attacker artifacts — QA'd lures, three tested CVEs, and 2,384 confirmed launch hits against Mexican targets.
Trend Micro: 'bandcampro' ran botnet ops through Gemini CLI
Trend Micro forensicated 200 Google Gemini CLI sessions used by a lone Russian-speaking actor to run an eight-node dental-clinic botnet through natural-language prompts.
ServiceNow AI Platform RCE exploited in wild: CVE-2026-6875
Threat-intel firm Defused reports active exploitation of ServiceNow AI Platform CVE-2026-6875, a week after ServiceNow said it saw none.
Hugging Face confirms breach by autonomous AI agent
Hugging Face disclosed unauthorized access to internal datasets and service credentials by an autonomous agent framework that ran thousands of sandboxed actions across a weekend.
wp2shell: first signs of exploitation; CVE-2026-60137 lands
watchTowr reports first signs of in-the-wild exploitation of the WordPress Core wp2shell RCE. The pending companion CVE-2026-60137 SQLi has landed, and exact patched versions are 6.9.5 and 7.0.2.
Two indicted over $43M laundered from investment scams
DOJ charged two New York-based Chinese nationals with laundering $43M in investment-fraud proceeds through 140 bank accounts and roughly 45 shell companies.
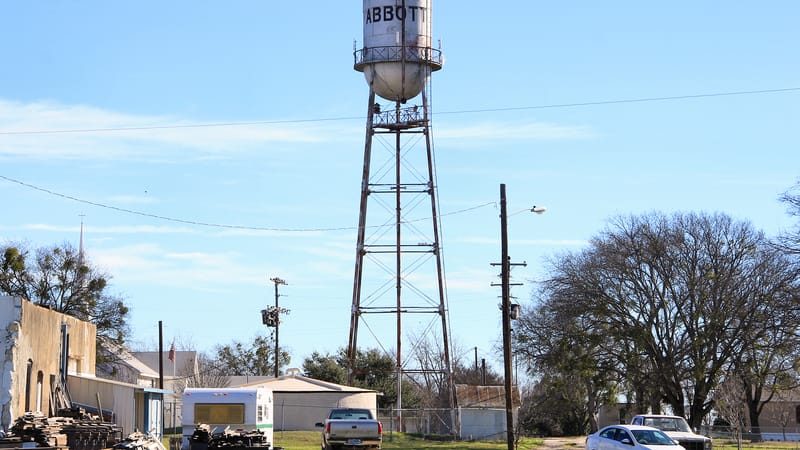
Abbott confirms Exact Sciences hit; LabCentral disputed
ShinyHunters used vishing to hit legacy Exact Sciences systems in Abbott's Cancer Diagnostics business; a separate LabCentral extortion claim by ShadowByt3$ is disputed.
WordPress Core RCE (wp2shell): CVE-2026-63030, PoC public
A critical unauthenticated remote code execution flaw in WordPress Core got a CVE, a GitHub advisory, and a working public PoC on July 17, 2026.
EU order opens Android mic, cam, screen to rival AI agents
EC ordered Google to open Android's mic, camera, screen, and always-on hotword to rival AI assistants — mandatory in Android 18 by 1 August 2027.
EY discloses breach via third-party IT ticket system
Ernst & Young says an unauthorized party accessed a third-party support ticket platform used by its IT staff between March 28 and April 12. Detection followed on April 23; disclosure landed July 17.
Armenia detains Aleksandr Ermakov on US REvil warrant
Russian tourist Aleksandr Ermakov has been held in Yerevan since 2026-06-28 on a US extradition request for a REvil suspect of the same name. His lawyer says the paperwork carries no patronymic.
GoSerpent: Go RAT hits APAC gov, TetrisPhantom overlap
Kaspersky documents GoSerpent, a Go-based RAT hitting Southeast Asian government and diplomatic entities since late 2025. Operational overlap with TetrisPhantom.
LegacyHive: unpatched Windows LPE zero-day, PoC public
Researcher Nightmare Eclipse dropped LegacyHive — an unpatched Windows User Profile Service LPE — hours after July Patch Tuesday. No CVE, PoC on GitHub.
Windows Server 2022 mainstream support ends Oct 13
Microsoft's Windows Server 2022 leaves mainstream support October 13, 2026 — but extended support runs five more years with security updates at no extra cost.
UAT-11795 hides Starland RAT in trojanized installers
Cisco Talos names UAT-11795 — a financially motivated Russian actor pushing Starland RAT and bespoke WLDR C2 via trojanized WebEx, Zoom, MobaXterm installers.
Elastic: TELEPUZ ClickFix stealer confirmed since April
Elastic Security Labs pins TELEPUZ, a modular C stealer spreading via ClickFix since late April, likely MaaS, with a Go Vidar variant as stage two.
Coca-Cola halts Fairlife US production after ransomware
Coca-Cola disclosed a Fairlife ransomware attack via SEC 8-K on July 16. US dairy production suspended, Canada unaffected. No group has claimed it.
ClickLock macOS stealer kills apps until user types password
Group-IB documents ClickLock, a macOS stealer delivered via ClickFix that kills Finder, Dock, and browsers on a 210ms loop until the victim types their login password.
23andMe settles genetics breach: $18M, 43 states
Multistate AG coalition led by New York's Letitia James. Settlement resolves claims over the 2023 credential-stuffing breach that exposed 6.9M customers' genetic profiles.
Spirals ransomware: full network encrypted in under 24h
Symantec documents Spirals, a new ransomware family: IIS web-shell entry to a fully encrypted network in under 24 hours — one confirmed victim so far, an IT services firm in South Asia.
OpenAI discloses GPT-Red, its internal automated red-teamer
OpenAI describes GPT-Red, an internal automated red-teamer that scales prompt injection discovery and adversarially trains later models against those attacks.
Dutch bust €100M fraud ring, 20 call centers, 700 shills
Dutch Politie takedown of a 2021-active investment-fraud ring — 20 call centers, ~700 fake advisers, five-country arrests, €100M+ estimated peak monthly.
Unit 42: TuxBot v3 shipped LLM chain-of-thought in comments
Palo Alto Unit 42 documents TuxBot v3, an IoT botnet whose developer left an AI safety disclaimer and raw reasoning traces in the shipped binary.
Kaspersky: OkoBot phishes seeds inside Ledger, Trezor apps
Kaspersky's GReAT team says OkoBot has hooked Electron in Ledger and Trezor apps since April 2025 to draw a fake seed-phrase prompt inside the real wallet UI.
LegacyHive: Chaotic Eclipse's fourth Windows zero-day
Researcher 'Chaotic Eclipse' released LegacyHive, a Windows User Profile Service arbitrary-hive-load LPE PoC, hours after July Patch Tuesday. Unpatched.
Miasma loader shipped in 5 @asyncapi npm package versions
5 @asyncapi npm versions unpublished. Miasma loader ships 744 modules over six C2 channels. Attackers compromised the CI/CD pipeline, not npm tokens — treat as post-install compromise.
DOJ indicts Media Land trio: LockBit, BlackSuit, Play host
USAO-NDOH unsealed a Dec 2024 indictment against Volosovik ('Yalishanda'), Pankova, and Zatolokin — Media Land and ML.Cloud hosted LockBit, BlackSuit, Play. $62M losses, 21 states.
Jalisco kit auto-refreshes M365 device codes on demand
ReliaQuest maps two new M365 phishing kits: Jalisco auto-refreshes OAuth device codes to defeat the 15-min window, OmegaLord harvests phones for MFA bypass.
Blackpoint flags LabubaRAT: Rust MaaS RAT poses as NVIDIA
Blackpoint Cyber's Sam Decker and Nevan Beal document LabubaRAT — a Rust MaaS trojan on Windows that ships as nvidia-sysruntime.exe with runtime config.
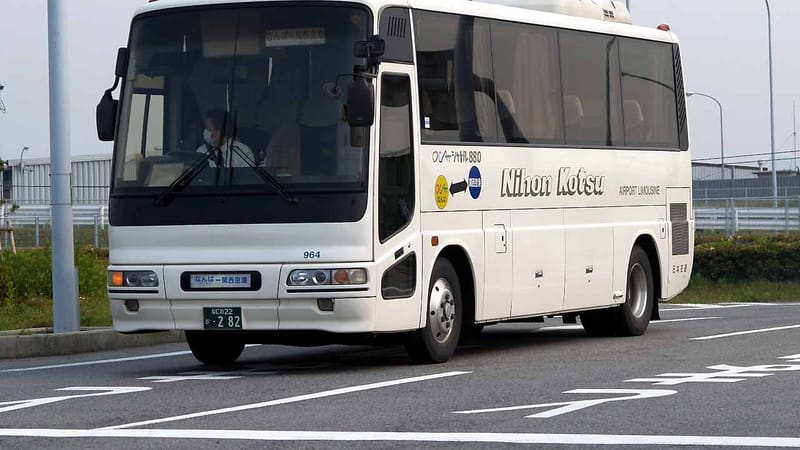
Nihon Kotsu cyberattack takes Japan taxi dispatch offline
Japan's largest taxi operator says a July 12 malware intrusion knocked dispatch, web booking, and labor-taxi services offline. No group has claimed.
ModHeader carried a dormant collector to 1.6M installs
Stripe OLT found a browsing-history collector inside the store-signed ModHeader extension. Edge pulled it July 3; Chrome pulled it July 10. The allow-list shipped empty.
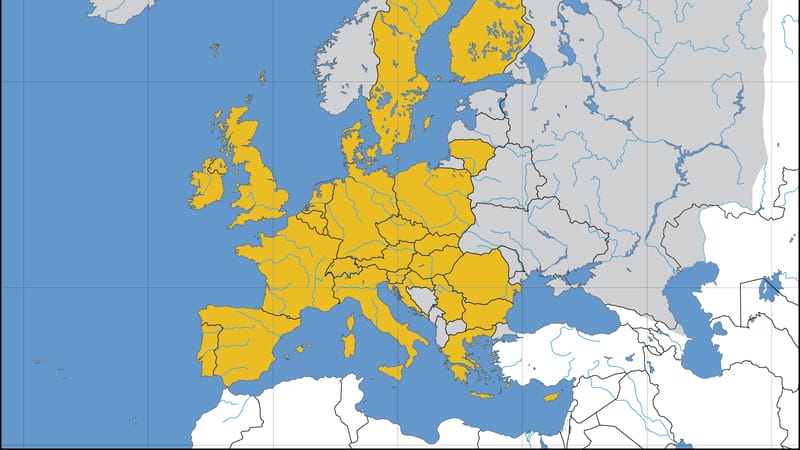
Lidl online shop breach hits DE, BE, NL via provider
Lidl says a file at an unnamed service provider was accessed; DE/BE/NL online shop customer PII taken. Passwords and payment data not yet ruled out.
First joint EU-UK cyber sanctions name 33 Russian targets
The EU Council named 9 individuals and 4 entities; the UK named 24 more. FSB Center 16, Sandworm, Turla, Lumma Stealer, and Rybar LLC are on the list.
Ill Bloom: Weak PRNG Drained $5.1M From Crypto Wallets
Coinspect's Ill Bloom disclosure: five unnamed wallets shipped seed-phrase code with weak randomness. Two sweeps in May and June drained $5.1M.
Helix: new data-extortion crew hits SharePoint via vishing
ReliaQuest attributes new data-extortion crew Helix to vishing and device-code phishing against SharePoint. Infrastructure overlaps BlackFile.
GigaWiper/BLUERABBIT: Go-based wiper, CyberAv3ngers-linked
Microsoft and Binary Defense concurrently disclose a Go-based Windows destructive backdoor — wipe, fake ransomware, spyware in one binary — attributed to Iran-nexus CyberAv3ngers.
GodDamn ransomware: Beast rebrand, signed EDR-killer driver
Symantec attributes a new family, GodDamn, as a Beast rebrand shipping the PoisonX driver (g11.sys) — a Microsoft-signed kernel BYOVD used to neutralize endpoint defenses.
INTERPOL First Light 2026: 5,811 arrests, $293M seized
INTERPOL's Operation First Light 2026 arrested 5,811 fraud suspects across 97 countries, seized $293M and blocked 31,014 accounts over 3.5 months.
AssuranceAmerica breach: 6.9M drivers, 4-month notice gap
AssuranceAmerica confirms a March 16 intrusion exposed data on 6,998,886 drivers. Notification letters went out in July — a nearly four-month gap between detection and public notice.
Mount Royal University confirms June breach, 30 BTC demand
Mount Royal University confirms a June 17 intrusion exfiltrated H drive data. A group calling itself CMD demands 30 BTC before the stated leak deadline.
Pink Vishing Enrolls Rogue Entra Passkeys on M365 Tenants
Okta and Unit 42 attribute an ongoing vishing campaign — active since April — that walks Microsoft 365 users through enrolling a passkey the attacker controls.
SCMBANKER active against Mexican banks — Elastic REF6045
Elastic Security Labs is tracking SCMBANKER (REF6045), a PowerShell fraud toolkit hitting Mexican banks, fintechs, and crypto exchanges via ClickFix lures.
KDDI Breach: 12M Emails, 7.6M Passwords via 3rd-Party 0day
KDDI says a May 16 zero-day in unnamed third-party software exposed 12,233,087 email addresses and 7,616,173 passwords across five Japanese ISPs.
CISA: Patch ColdFusion CVE-2026-48282 by Friday
CISA added Adobe ColdFusion CVE-2026-48282 to KEV on July 7 and set a July 10 federal patch deadline under BOD 26-04. CVSS 10.0. Actively exploited.
DEBULL Kit Runs M365 Device-Code Phishing, Storm-2372
ZeroBEC reports DEBULL — a device-code phishing kit repackaging Storm-2372 tradecraft — active against M365 tenants late June to early July. Block it.
China-Linked UAT-7810 Expands ORB Net With LONGLEASH
Cisco Talos ties China-aligned UAT-7810 to LONGLEASH backdoor and an expanding ORB relay network built on unpatched Ruckus and ASUS routers.
Accenture Confirms Breach; Attacker Claims 35 GB Stolen
Accenture confirmed a security incident. A threat actor is advertising 35 GB of alleged source code for sale. The volume claim is unverified — treat accordingly.
DragonReturn Drops DcRAT on Indian Taxpayers
Seqrite Labs attributes an ongoing spear-phishing campaign against Indian tax filers to a suspected China-nexus actor with infrastructure and tactical overlap to Silver Fox. First observed May 18.
Kairos Took $1M — and Never Encrypted a File
Ransom-ISAC's new case study confirms a ~$1M payment (9.44 BTC) to the Kairos crew on June 13, 2025. Krishnan's review found no encryption at any point — data-theft extortion only, tracked in ransomware feeds anyway.
BlueHammer Defender LPE Now Used in Ransomware
CVE-2026-33825, the Microsoft Defender local privilege escalation disclosed as a zero-day by 'Chaotic Eclipse' in April, is confirmed weaponized in ransomware. Patched. Ransomware family unnamed.
Avalon Framework Bundles Theft, Wiper, CrownX
Blackpoint Cyber says the previously undocumented Avalon framework combines credential theft, EDR-aware defense evasion, shadow-copy destruction, and the CrownX ransomware payload in one multi-stage phishing chain.
FortiBleed Tied to INC and Lynx Ransomware Crews
The Hacker News reports an operator behind FortiBleed's credential-theft infrastructure was seen running ransomware negotiation panels for both INC and Lynx. Not a resale ring — a pipeline.
Sysdig: JADEPUFFER ran a full ransomware chain from one LLM
Sysdig's Threat Research Team says JADEPUFFER is the first ransomware incident it has observed where an AI agent handled entry, credential theft, lateral movement, and destruction end-to-end. Initial access was a Langflow code-execution flaw.
Blackpoint: Avalon Bundles Theft, Wiper, CrownX
Blackpoint Cyber documents Avalon, a previously undocumented modular framework whose ransomware payload — CrownX — arrives at the end of a legal-lure phishing chain that stages through Proton Drive, ISO, LNK, and MSBuild.
Anubis Ransomware Exploits Citrix Bleed 2
The Hacker News reports Anubis-ransomware affiliates using Citrix Bleed 2 (CVE-2025-5777) to breach NetScaler-fronted environments, then pivoting with legit RMM, BYOVD, and stolen supply-chain credentials.
FBI Seizes NetNut Proxy, Google Degrades Popa Botnet
The FBI seized hundreds of NetNut proxy domains on July 2; Google's Threat Intelligence Group, working with FBI and Lumen, cut the linked Popa botnet's usable device pool by millions the same day.